Certificate management that automatically controls access rights.

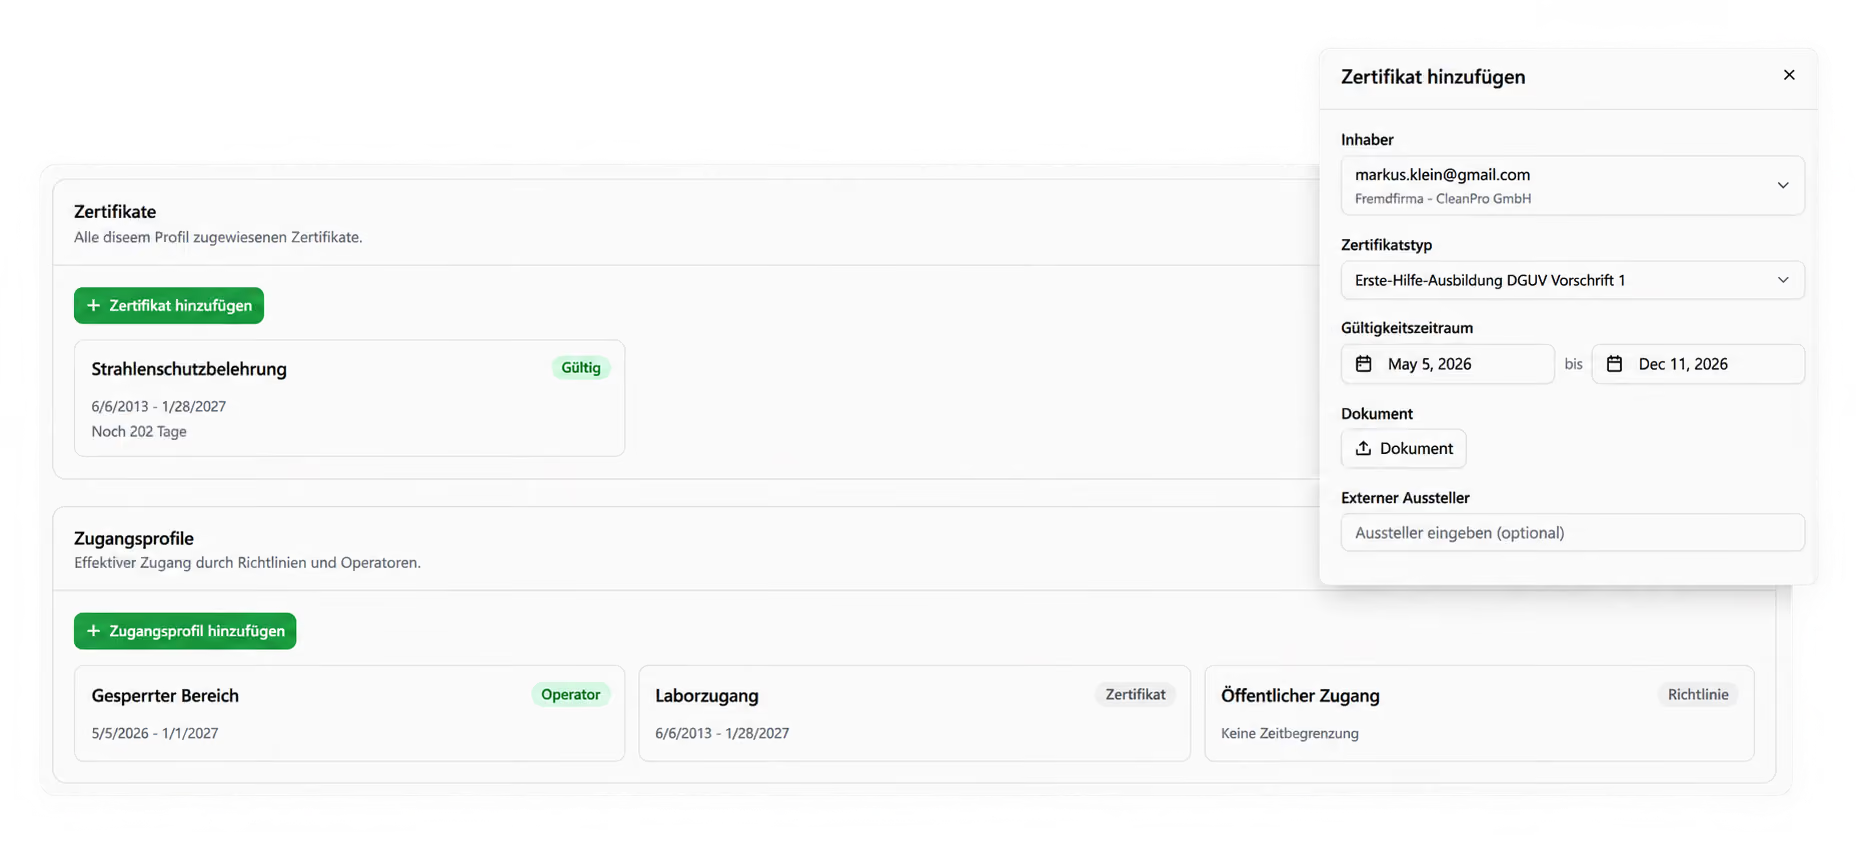
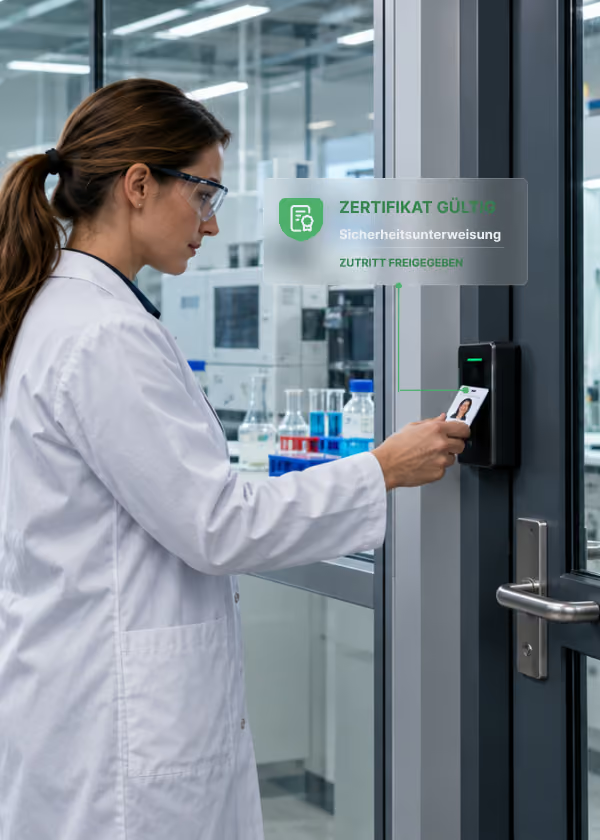
IDfunction PIAM links certificates with physical access permissions. Rights are automatically granted or revoked based on certificate validity. Every change is documented.
Reduced administrative effort with
‍IDfunction PIAM

Maintain a clear overview, even with a large number of employees, certificates, and locations.
01

Store certificate

Record qualifications, validity, and proof.
02

Define access

Link the certificate with the appropriate access profile.
03

Automated control

Send renewal reminders, update access rights, and revoke them upon expiration.
04

Fully traceable

All changes are documented.

Proven in industry and critical infrastructure.

"As an operator of critical infrastructure, we require complete transparency and control over physical identity and access management. The PIAM solution from evolutionID provides us with structured, workflow-driven processes that improve security, compliance, and efficiency."

Dirk Kleinert
Technical IT & Systems │ Stromnetz Berlin GmbH

"As a global company with diverse systems, we needed to harmonize our access processes while maintaining the highest security standards. With evolutionID, we have created a central platform that integrates all systems and enables transparent identity and access management worldwide—scalable, automated, and future-proof."
Adil Sahin
Head of IT Infrastructure | thyssenkrupp Spring & Stabilizers

Less effort. More control

vs
A circle with a checkmark.
Centralized certificate tracking
A circle with a checkmark.
Automatic reminders
A circle with a checkmark.
Automatically update rights
A circle with a checkmark.
Automatic revocation
A circle with a checkmark.
Documented changes
Manual management
Managing certificates in Excel
Tracking deadlines yourself
Manually adjusting access rights
Access despite expired certificates
Scrambling for documentation

Close the gap between certificates and access.

Let's take a look together at where your current process is creating risks and unnecessary effort.
Discuss certificate management

Let's talk about your process.

How do you manage certificates and their associated access rights today?